Connect your Microsoft Azure account to manage clusters, access registries, or use other integration features.
To add your Azure account, open Cloud → Provider links. If you already have provider links, select Create provider link. Otherwise, select Add provider link beside your provider.
After connecting the account, continue to registry setup or cluster creation.
Add your Azure account
Create a Microsoft Entra ID application to connect your Azure subscription to Northflank.
You will need the following to get started:
- Permission to register applications and create client secrets in Microsoft Entra ID
- Permission to assign roles on the subscription, such as Owner or User Access Administrator
- For cluster deployment: sufficient quotas to deploy your cluster
If your tenant restricts application registration, Application Administrator or Cloud Application Administrator can provide the required application permissions.
Start the integration in Northflank
- Open Cloud → Provider links in Northflank.
- Open the Azure provider link form .
- Under Basic information, enter a Name.
- Select the features you need under Desired features.
For registry access, select Docker Registries and, for project builds, Docker Registry Push. Select BYOC only if this integration also manages clusters.
Register an application in Entra ID
Copy each requested value into Credentials in Northflank as you complete these steps.
- Open Microsoft Entra ID in the Azure portal .
- Open App registrations and register a new application .
- Copy the directory (tenant) ID and application (client) ID into Northflank.
- Open the link for Managed application in local directory.
- Copy the object ID from that application's properties into Northflank.
- Return to the application registration and open Certificates & secrets.
- Create a client secret and copy its value into Northflank.
Use the secret value, rather than its ID.
Grant the application access to your subscription
The Northflank Azure integration requires the Contributor role on the connected subscription, including for registry use. Registry pull and push roles alone do not replace this integration requirement.
- Open Subscriptions in Azure and select the subscription to connect.
- Open Access control (IAM) and add a role assignment.
- Select the Contributor role .
- Under Members, select User, group, or service principal.
- Select your application's service principal and save the assignment.
- For cluster deployment, open Resource providers and register
Microsoft.ContainerService. - Copy the subscription ID into Subscription ID under Credentials in Northflank.
- Select Create provider link.
For registry use, connect an existing Azure Container Registry in this subscription. The registry uses the Microsoft.ContainerRegistry resource provider. See Azure resource provider registration if Azure reports a registration error.
For cluster deployment, continue to quotas and cluster creation.
You can update the integration's credentials when required.
Keep access to existing resources when you replace credentials. Without that access, Northflank cannot manage those resources, and deleting clusters directly in Azure can leave unused resources.
Check your quotas
To successfully deploy a cluster on Azure using Northflank you must have the required resources available to your account for your desired region.
Check the node types you wish to deploy and ensure your cluster has access to the relevant resources. The specific quotas for each provider may differ, you will need to ensure you have sufficient quotas for your required node type, vCPU, and disk type for your desired regions.
Check and edit your Azure subscription quotas from the usage + quotas page of the relevant subscription. You can filter the quotas by provider as well as region.
For example, to increase the number of node pools you can deploy on Azure using the Standard_D2ds_v5 node type you should select the resource provider compute, filter quotas by your cluster's region, select Standard DDSv5 Family vCPUs from the list, and request a quota increase. This will also automatically increase your Total Regional vCPUs quota, if the request is successful.
Create a cluster
To add a new cluster, navigate to the clusters page in your account settings and click create cluster.
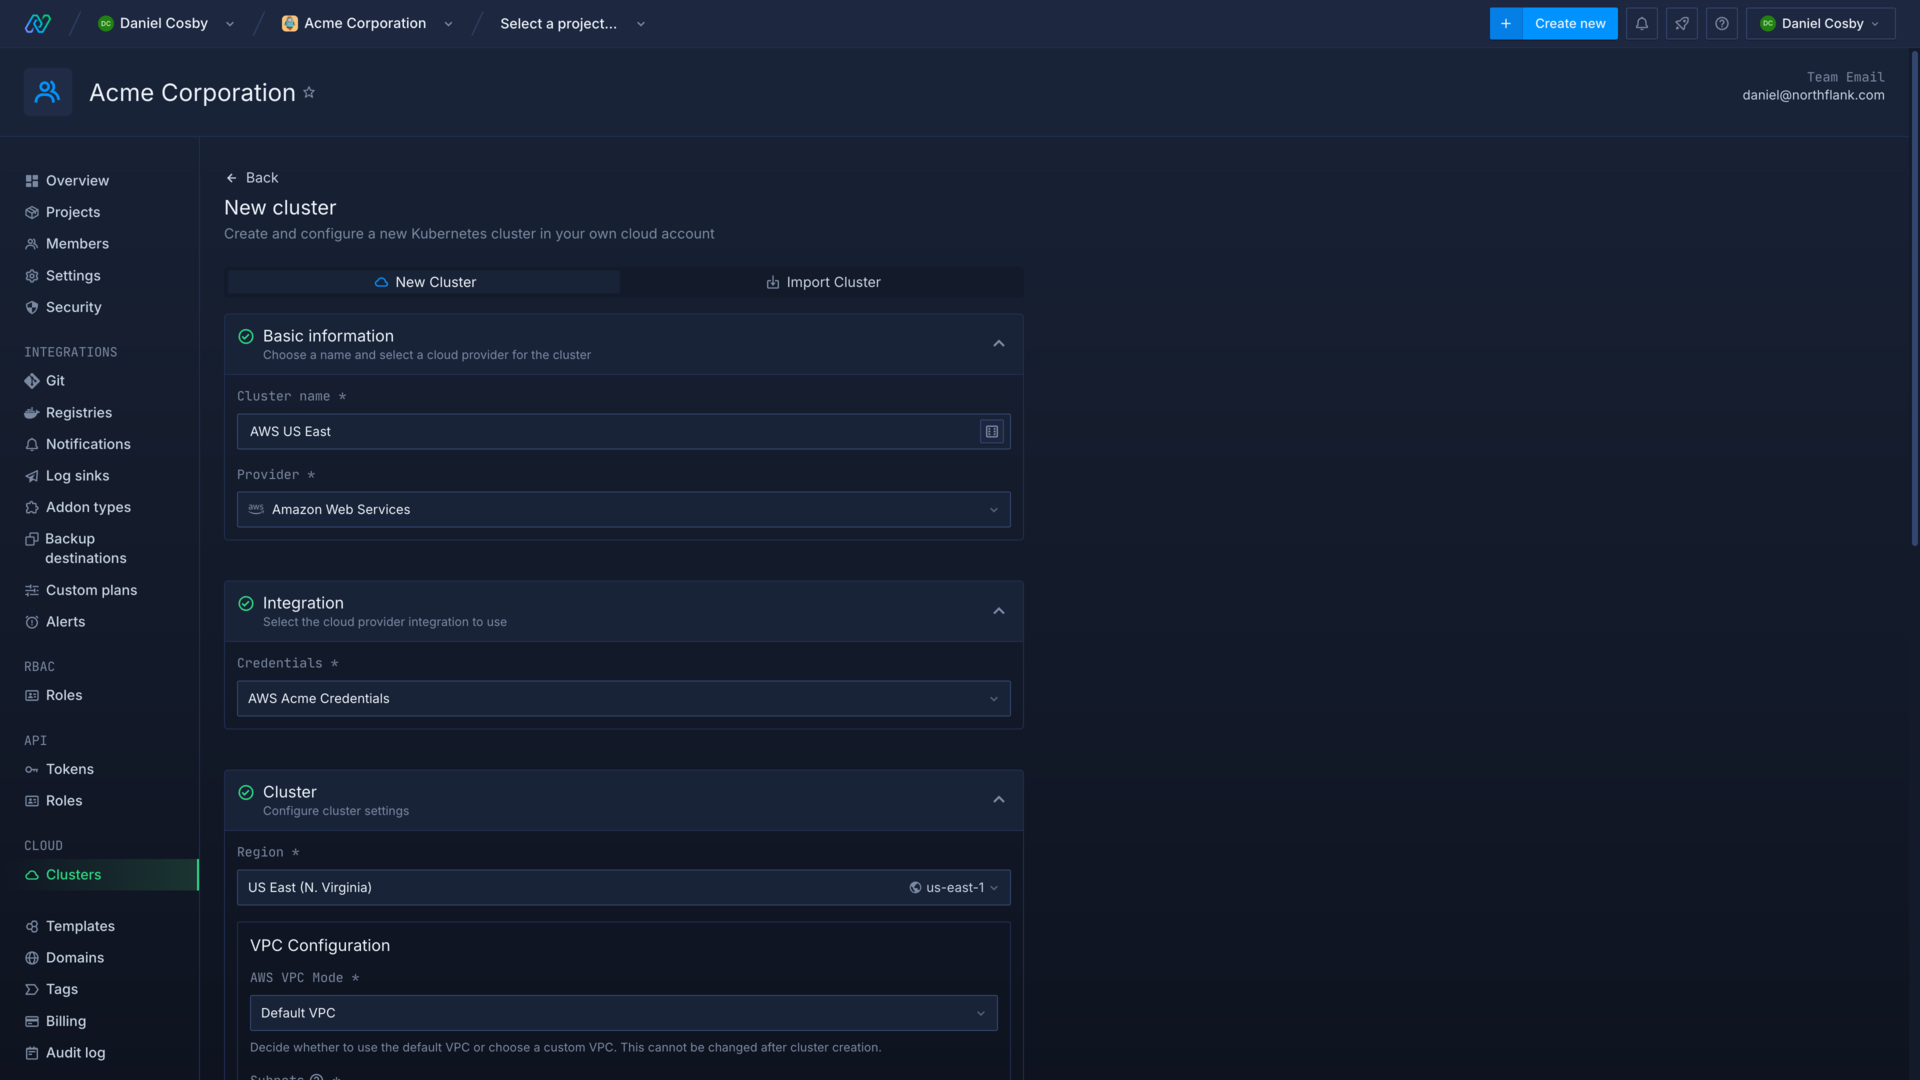
Enter a name for the cluster and select Azure as the cloud provider. Choose your integration credentials and select the region to deploy in.
Configure node pools
You can now configure the node pools for your cluster. Node pools can also be added, deleted, and updated after creating your cluster. Click add node pool to add another pool.
Each cluster requires at least one node pool, and a combined minimum of 8 vCPU and 16GB memory across all node pools.
One node pool must be assigned as the system node pool to schedule non-user workloads. For best performance you should assign it more than one node and disable autoscaling.
Each node can schedule up to 250 pods (minus system pods). The actual number of pods per node will usually be limited by resource requests and request modifiers for smaller nodes.
Cluster networking limits
The number of workloads that can be deployed to an AKS cluster is limited by the available number of pod and service IP addresses, allocated by CIDR block.
AKS clusters allocate a CIDR block of /16 for pods and services, which means you can deploy thousands of services and pods to your cluster without facing networking constraints.
See deploy and scale node pools for more information on configuring nodes and node pools.
Configure advanced options
After adding your initial node pools you can configure advanced options for the cluster, such as build infrastructure and resource request modifiers.
When you create the cluster Northflank will begin installing system components in node pools according to their capacity. This may take up to 20 minutes.
Deploy to private nodes
Azure AKS nodes have no public IP addresses by default. This prevents direct connections from the internet to the nodes. Workloads on private nodes can still receive traffic through an ingress load balancer.
Northflank installs public ingress by default. Eligible clusters can use private ingress or both paths. See Public and VPC ingress for availability and configuration.
Next steps
Configure your Kubernetes cluster
Deploy node pools
Deploy workloads to your cluster
Run GPU workloads